CrowdStrike
Stop breaches by strengthening your security operations.
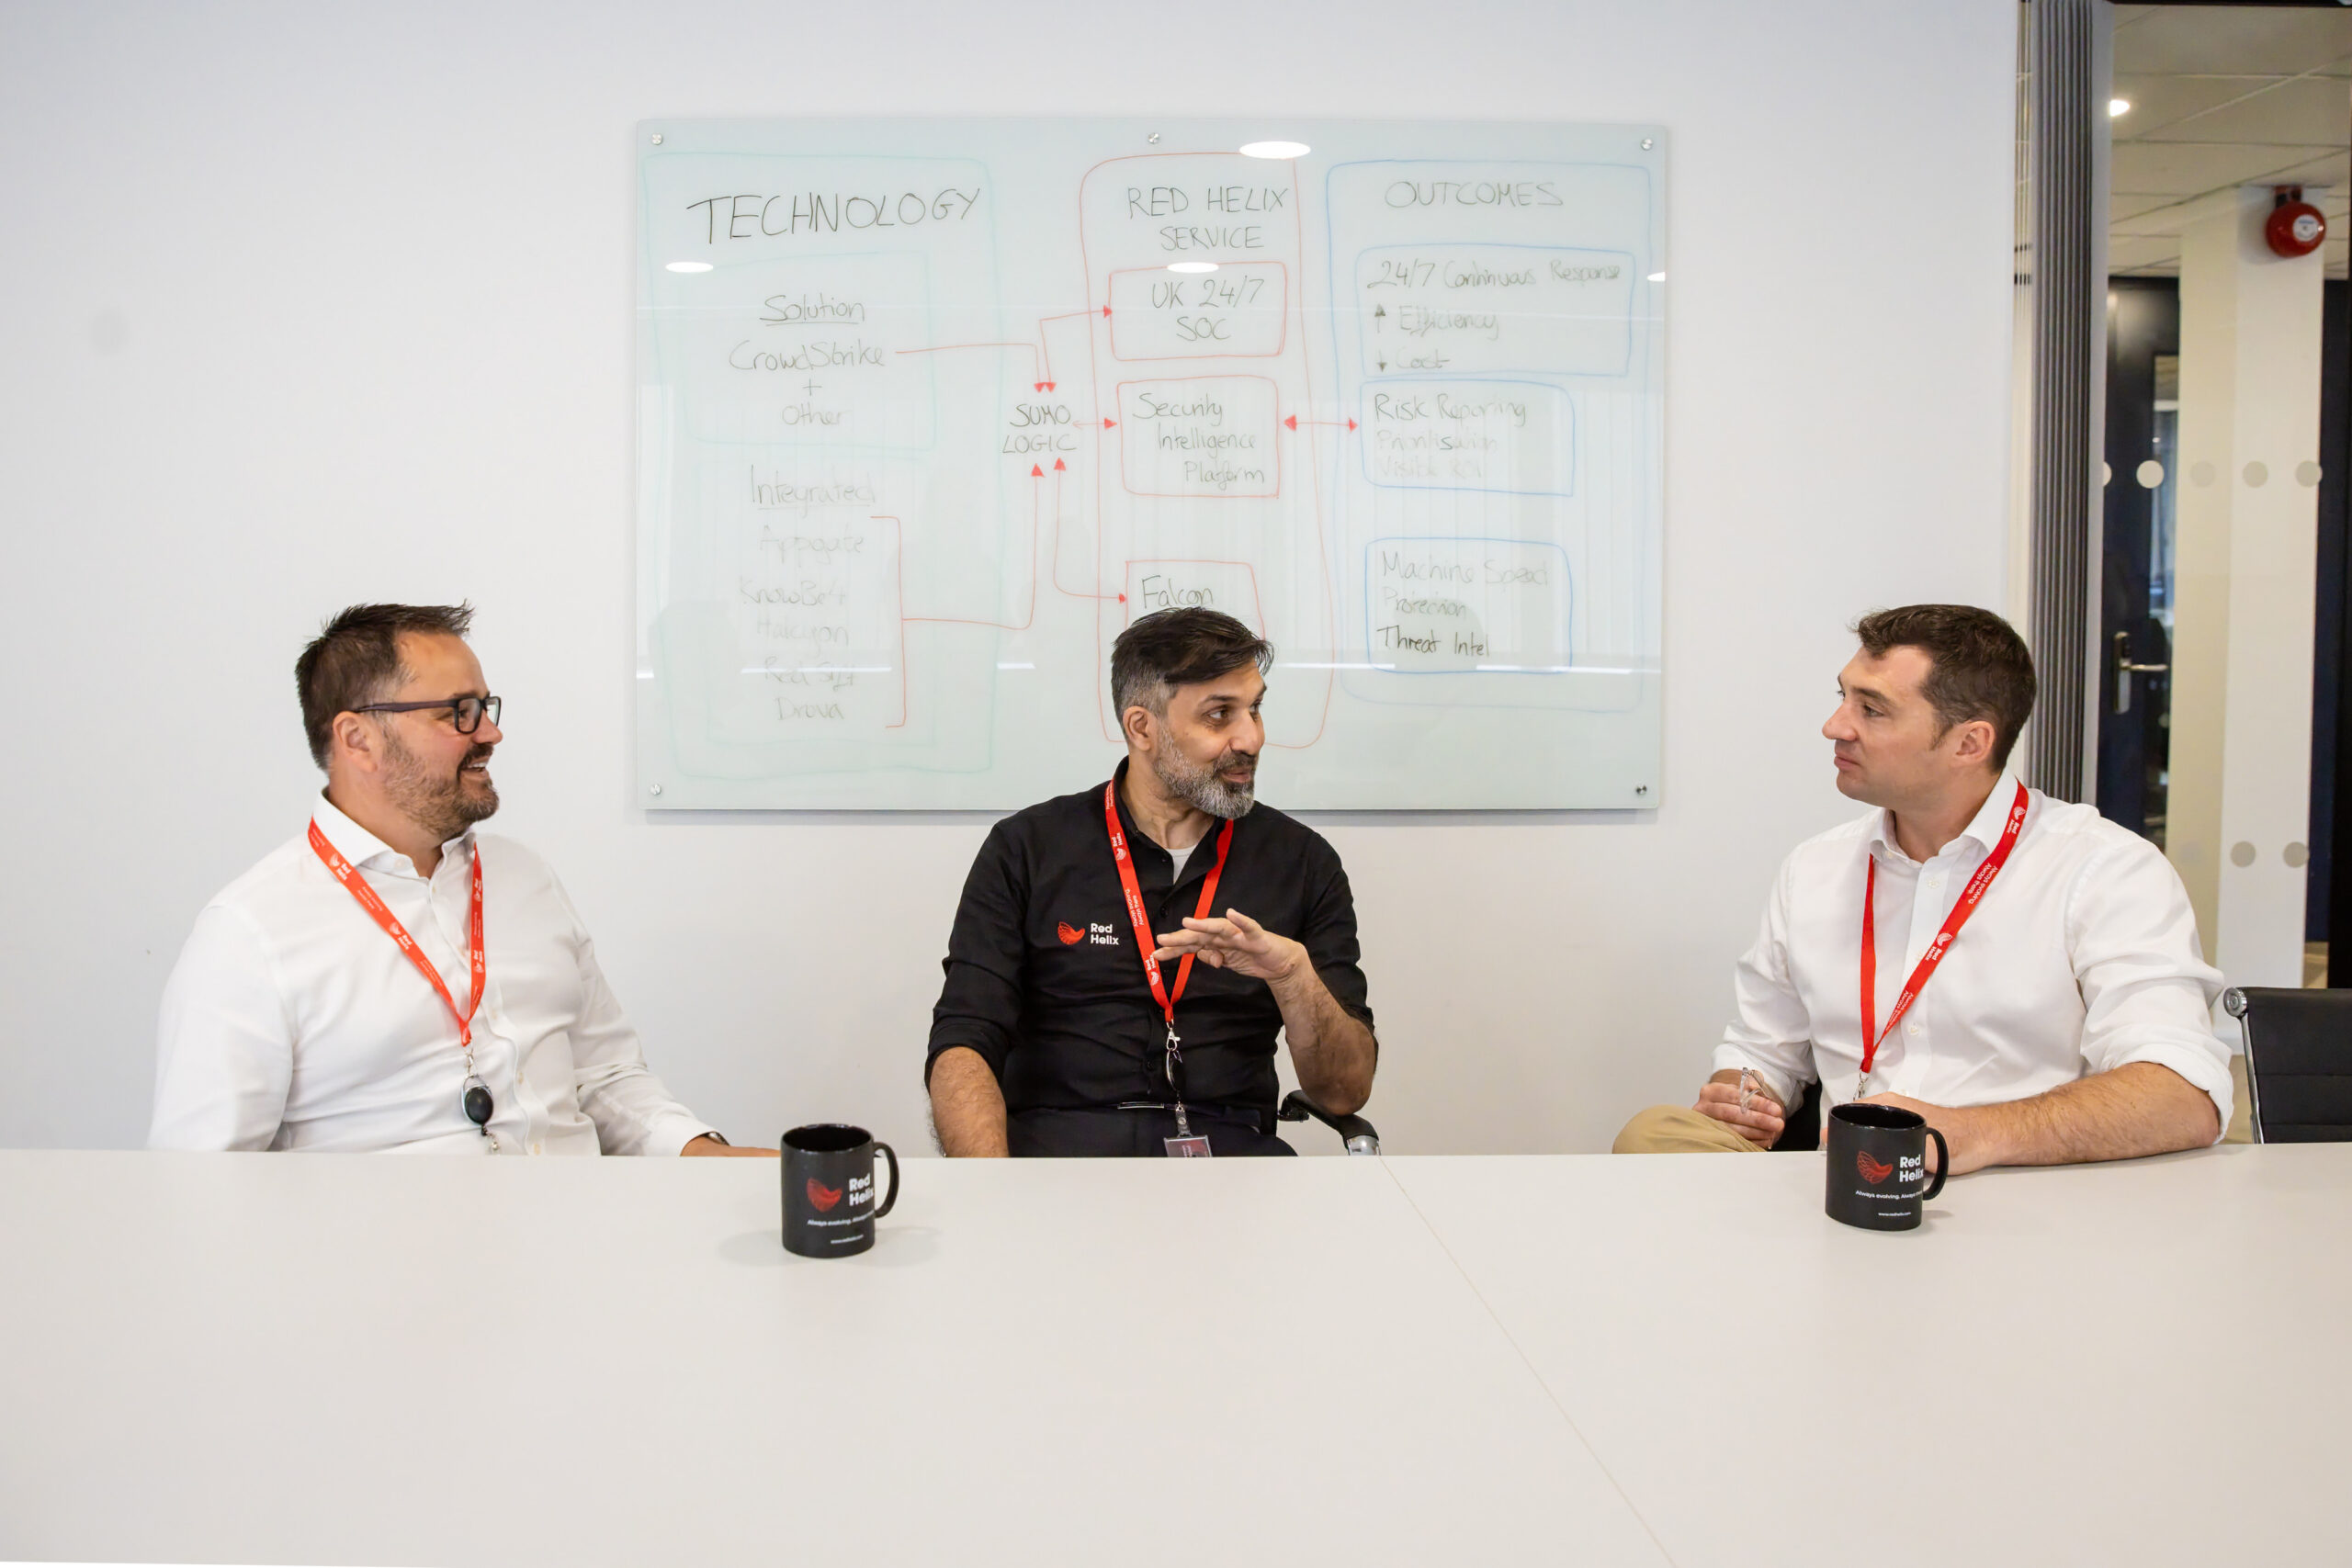
Red Helix combines the CrowdStrike Falcon platform with 24/7 monitoring and cyber security expertise from our UK-based Security Operations Centre.
We help organisations detect, investigate and contain threats across endpoints, identities, mobile devices and emerging AI attack surfaces, while reducing the operational burden on internal IT and security teams.
One Platform. One Security Partner.
CrowdStrike provides a unified, AI-native security platform built to protect organisations against modern adversaries. Red Helix provides the people, monitoring and operational capability to help you get maximum value from that technology.
With Red Helix, you benefit from:
- 24/7 security monitoring from a UK-based SOC
- Rapid threat triage and escalation
- Continuous detection and response
- Expert security analysts and incident support
- A managed service built around your existing security operations
- Clear accountability across technology and security operations
The result is a security service designed to help you reduce risk without building and operating every capability internally.
Managed CrowdStrike Security
Protect the endpoint by stopping breaches
From deployment to day-to-day security operations, Red Helix can manage your CrowdStrike environment, including configuration, monitoring, investigation, incident escalation and ongoing service management.
| Endpoint Protection | Falcon Prevent | Next-generation antivirus and endpoint prevention. Detects and blocks malware, ransomware and other malicious activity on endpoints. |
| Threat Detection | Falcon Exposure Management | Identifies and prioritises exposures across the environment, helping customers understand where security risk is concentrated. |
| Threat Detection | Falcon Adversary OverWatch | CrowdStrike's specialist threat hunters use AI and adversary intelligence to proactively search for sophisticated threats that automated controls may not identify on their own. |
| Threat Detection | Falcon Adversary Intelligence | Falcon Adversary Intelligence optimizes effectiveness through automated intelligence orchestration, contextual enrichment and AI-powered investigative tools. |
| Managed Devices | Falcon Device Control | Gain visibility and control over removable media devices, including USB storage and other connected devices. |
| Managed Devices | Falcon Firewall Management | Centralise visibility and management of endpoint firewall policies. |
| Managed Devices | Falcon for Mobile | Detect malicious activity and reduce mobile security risk across supported Android and iOS environments. |
| Managed Devices | Falcon Discover for IoT | Falcon Discover for IoT eliminates XIoT blind spots to proactively stop breaches, helps break ICS environment silos and delivers superior ROI from a trusted and easy-to-manage platform. |
| Managed Devices | Falcon FileVantage | File integrity monitoring solution that simplifies the security stack and provides real-time insight for file changes. |
| Managed Devices | Falcon Shield | CrowdStrike Falcon Shield's SaaS security platform empowers you to prevent, detect and respond to SaaS threats. |
| Identity Protection | Falcon Identity Protection | Detects and responds to identity-based threats, including compromised credentials and suspicious identity activity. |
| Identity Protection | Falcon Privileged Access | Falcon Privileged Access enforces just-in-time access to stop identity attacks, delivering real time, risk based privileged access control across hybrid environments. |
| AI Protection | Falcon AI Detection and Response | CrowdStrike Falcon AI Detection and Response provides visibility and protection across AI usage, prompts, models, agents and related workloads. |
| AI Protection | Charlotte AI | Charlotte AI is the brain of the agentic SOC helping to automate repetitive tasks and accelerate outcomes. |
| Cloud Security | Falcon Cloud Security | Broader cloud security covering cloud workloads, containers, applications, identities, data and cloud posture. |
| SIEM | Falcon Next-Gen SIEM | Correlates security data from CrowdStrike and third-party sources to support detection, investigation and SOC operations. |
Why Choose Red Helix for Managed CrowdStrike?
CrowdStrike provides the platform, Red Helix helps you operate it. Our managed service is designed for organisations that want access to advanced security technology without carrying the full operational cost of building, staffing and maintaining every security capability internally.
Security analysts monitor and triage your environment around the clock.
Security alerts are assessed promptly so potential threats can be investigated and escalated.
Our security specialists manage and operate CrowdStrike capabilities as part of your wider security environment.
A single team to help manage your CrowdStrike security operations and wider security requirements.
Managed Security Across Your Environment
On any one platform there are multiple attack surfaces.
Your security strategy should not be limited to the endpoint. The CrowdStrike Falcon platform brings together security capabilities across multiple domains. Red Helix helps organisations apply those capabilities within a managed security operating model.
Managed CrowdStrike Without Unnecessary Disruption
Whether your environment is cloud-based, hybrid or on-premises, Red Helix helps manage the deployment and operation of CrowdStrike within your existing technology estate.
Get in touch| Seamless deployment |  |
| Security policy configuration | |
| Endpoint onboarding | |
| Continuous monitoring | |
| Threat triage and investigation | |
| Incident escalation and response | |
| Ongoing service reviews | |
| Alignment with your wider security operations | |
This allows internal teams to retain control of their security strategy while Red Helix provides additional operational capability.
Secure Your Environment with Red Helix and CrowdStrike
Modern cyber security is no longer just an endpoint protection decision. It is a decision about how your organisation brings together technology, threat intelligence and security operations to reduce risk across an expanding attack surface.
Red Helix combines CrowdStrike technology with UK-based 24/7 security operations to help organisations strengthen detection, investigation and response without building every capability internally.
Contact us
Talk to our CrowdStrike Experts
Get in touch